Microsoft 365 Security Health Check

Know where the security of your Microsoft 365, Entra and Intune environment stands. Measured against the CIS benchmark, the CISA baselines and Zero Trust, and, on the continuous plans, every day: with history, deviations, hardening advice and audit evidence.

Request a Health Check
Microsoft 365 Security Health Check

Insight you can
prove

Configurations change constantly: new policies, exceptions, administrators adjusting something. The Health Check shows where your environment deviates from a secure baseline and keeps track of it. We supplement the measurements with our interpretation and advice.

Measured against recognised standards

Checks across your complete Microsoft environment

Your configuration compared with the CIS Microsoft 365 Foundations Benchmark, the CISA baselines and Microsoft’s Zero Trust controls.

  • Entra ID: Conditional Access, MFA, admin roles and guest access
  • Intune and device management
  • Exchange Online, Defender for Office 365 and Purview
  • SharePoint, Teams and Azure

Continuously in view

Measured every day, with history going back years

With the continuous options you see not only where things stand now, but also how they develop.

  • Daily measurements of the configuration
  • Deviations from the previous measurement and the baseline
  • An alert as soon as something deteriorates
  • A history you can always look back on

From measurement
to evidence

A measurement is only valuable if you can act on it. That is why we translate the results into concrete steps and into evidence you can show.

CIS, CISA and Zero Trust

The checks follow the CIS Microsoft 365 Foundations Benchmark, the CISA security baselines and Microsoft’s Zero Trust model. So you know where you stand compared with what the market considers secure.

Hardening

We translate findings into concrete hardening steps, in order of risk. Implementation is done on an hourly basis: by us, or by your own team or IT partner with our support.

CIS, CISA and Zero Trust

Compliance and audit evidence

Every measurement is recorded. This lets you demonstrate how your environment stood at a given moment, as evidence for NIS2, the Dutch Cyber Security Act (Cyberbeveiligingswet, Cbw), ISO 27001 and the BIO (Dutch government information security baseline).

Risk register

Deviations you consciously accept are recorded with an owner, a reason and an end date. They no longer count as noise and automatically return after the end date.

Compliance and audit evidence

Dashboards that show where you stand

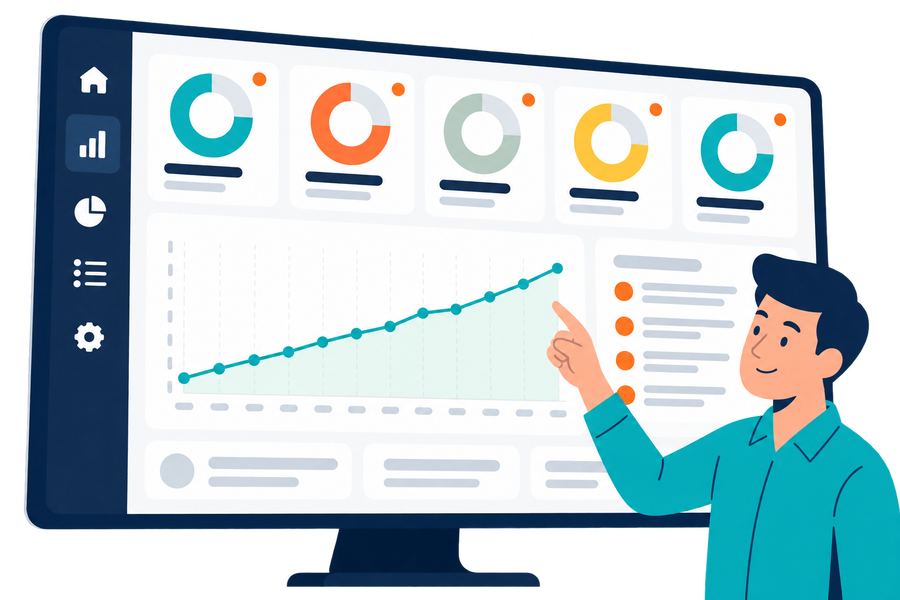
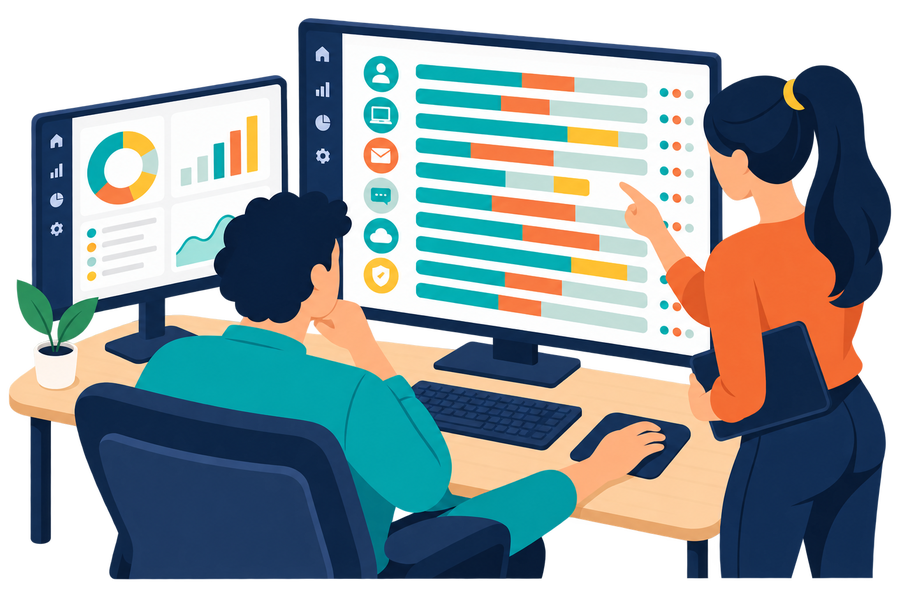
A score for the security of your environment, the trend over recent measurements and, per Microsoft product, how many checks pass, fail or do not apply. The items that need attention are at the top, and for each measurement you see exactly what has changed.

Dashboards that show where you stand
An alert whenever something gets worse

An alert whenever something gets worse

Every measurement is compared with the previous one. Does someone disable MFA for a group, or is an administrator added? You see it the next day and receive an email alert. Accepted risks do not trigger alerts.

Reporting in plain language

Not a technical list of hundreds of findings, but a report that shows what is going on, what the risk is and what you should address first. With the continuous options you receive a monthly report on how your environment is developing.

Reporting in plain language
Hardening by the hour

Hardening by the hour

Remediation work is never included in the fixed price, so you only pay for what you have done. We carry out the hardening, or support your own team or IT partner. The next measurement shows whether it has had an effect.

Choose what suits you

Every option starts with a baseline assessment. After that you choose whether to keep it to a snapshot, or to have your environment measured continuously.

One-off

Baseline assessment

A snapshot of your environment.

  • Full measurement against CIS, CISA and Zero Trust
  • Baseline and accepted risks recorded
  • Report with priorities and hardening advice
  • Discussion of the results

Price on request

Request

Continuous + expert

Monthly

Measurements plus a regular sparring partner.

  • Everything in Continuous
  • Monthly review of the results
  • Risk register
  • Audit evidence for Cbw/NIS2, ISO 27001 and BIO
  • A sounding board when implementing changes

Fixed price per environment per month, on request

Request

Hardening and other remediation work are not included in the fixed price. If you want us to resolve findings as well, this is done on an hourly basis.

Frequently asked questions

A scan gives you a list of findings at a single moment. The value of the Health Check lies in what happens around it: a baseline that fits your organisation, daily measurements with history, interpretation of the results and audit evidence in plain language.

Entra ID, Intune, Exchange Online, Defender for Office 365, Purview, SharePoint, Teams and Azure. Which checks apply depends on the licences and services you use.

No. The measurements only observe and change nothing in your environment. We sign a data processing agreement covering the processing of your data.

Hardening and other remediation work are not included in the fixed price. On request we carry it out on an hourly basis, or support your own team or IT partner.

The Health Check gives insight into the security of your Microsoft 365, Entra and Intune environment and, with the Continuous + expert option, provides audit evidence. That helps you demonstrate your duty of care, but it is not a full Cbw assessment of your organisation. Read more in our article Dutch Cyber Security Act: being secure is not enough.

Want to know where your environment stands?

Get in touch for a baseline assessment or an explanation of the options.
Get in touch